A file lands in your inbox from a trusted partner, through an approved channel, sent by someone your systems have already verified. Every access control did its job. And yet that file could still be carrying a threat that none of those controls were ever built to catch.
That's the blind spot hiding inside even the most mature Zero Trust strategies: organizations have poured resources into verifying who gets access, while the safety of what they're actually receiving has been left largely on the honor system. Today, Glasswall and Virtru are teaming up to address that gap by bringing content trust and persistent data protection together.
The problem: securing access isn't the same as securing content
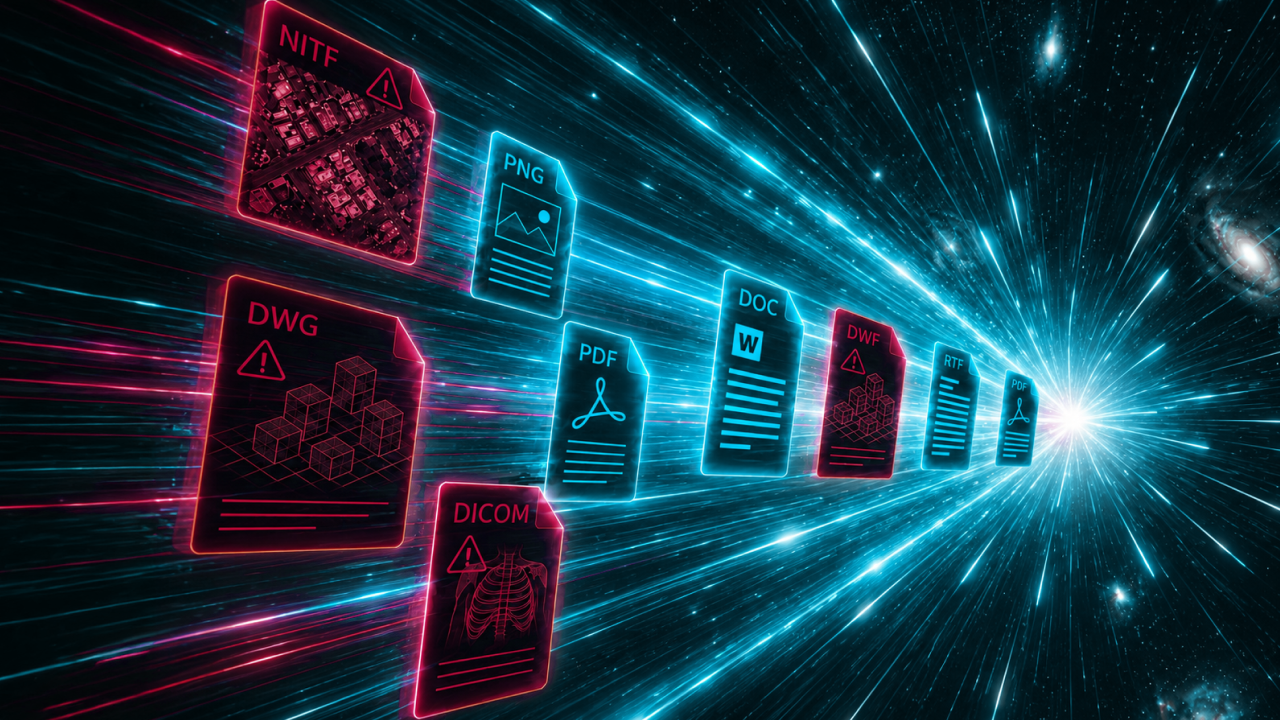
As government, defense, and enterprise organizations mature their Zero Trust architectures, most of the investment has gone into controlling who can reach a file. But files received through fully authorized channels, from fully authenticated senders, can still carry embedded malware, zero-day exploits, and malformed structures. Access control and content safety are two different problems, and a complete Zero Trust strategy needs to address both.
The joint solution: trusted content, controlled access
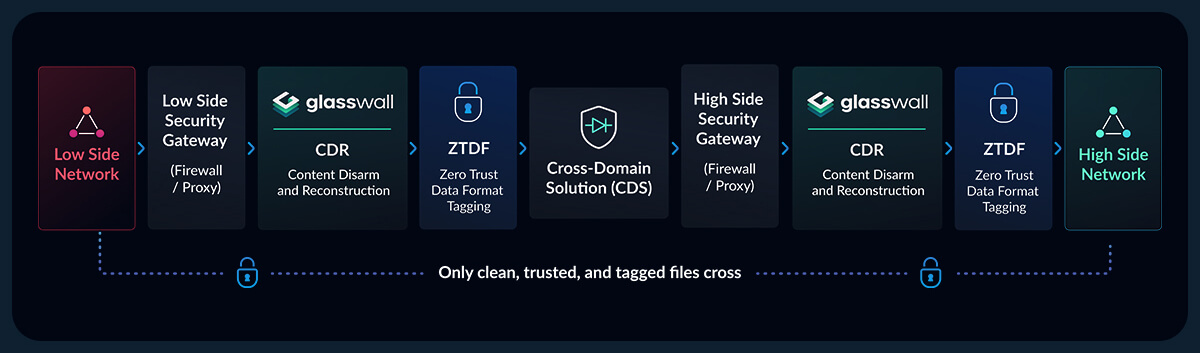
The partnership pairs Glasswall's deterministic Content Disarm and Reconstruction (CDR) with Virtru's Data Security Platform. Glasswall treats every file as untrusted and rebuilds it to known-good file specifications rather than scanning for known threats. Virtru wraps files in persistent encryption and policy-based access controls that travel with the data wherever it goes.
In practice, Glasswall acts as the policy enforcement point and Virtru as the policy decision point — a division of labor aligned with the Federal Zero Trust Architecture (NIST SP 800-207), the DoW Zero Trust architecture and roadmap, and ACP-240, the Five Eyes interoperability standard for the Zero Trust Data Format (ZTDF).
“Organizations need to be able to trust their data at every stage of its journey, not only who can access it, but whether the content itself is safe,” said Sam Hutton, Chief Growth Officer at Glasswall. “Our partnership with Virtru brings together two complementary approaches to data-centric security, helping customers share sensitive information with greater confidence while advancing Zero Trust across mission-critical environments.”
“Sanitizing a file and moving it across a trust boundary has traditionally meant losing cryptographic control of the file,” said Will Peppo, Senior Vice President of Business Development at Virtru. “With this integration, the file is rebuilt and re-encrypted with its policy-based protections remaining intact. Mission owners no longer have to choose between a file that is safe and a file that is still under their control.”
Where it matters
The combined approach is built for organizations exchanging sensitive information across trust boundaries, including:
Mission partner and coalition information sharing
Protection of sensitive government and defense data
Zero Trust data-layer security
Contractor and supply-chain collaboration
Cross-organizational file exchange
Files entering sensitive workflows and mission systems
Trust the content, not just the credentials
Zero Trust has always meant “never trust, always verify.” Glasswall and Virtru extend that principle to the file itself, so organizations no longer have to choose between securing access and securing content. Together, they create a stronger foundation for trusted data exchange across organizational and mission boundaries.
A co-founding executive with more than 20 years’ experience in the technology sector, he currently serves as Chief Growth Officer at Glasswall, a role he has held for over three years. Prior to this, he spent nearly seven years as Senior Vice President, building and scaling the company’s North American business. As CGO, he has driven sustained revenue growth by leading and developing high-performing sales organizations, fostering cross-functional collaboration and executing innovative go-to-market strategies.
See what Zero Trust file protection looks like. Live, in 25 minutes.
A tailored walkthrough of how Glasswall rebuilds files to a known-good state, removes hidden threats, and provides the intelligence you need to understand file risk.
What's in the demo
See malicious files rebuilt in real time Watch Glasswall remove hidden threats and return a safe, usable files.
Integrate security without disruption See how Glasswall fits into your existing workflows and infrastructure.
Gain complete visibility into file risk Uncover threats, anomalies and hidden file intelligence.
“
Beazley's security is paramount, and this integration has significantly reinforced our cybersecurity framework.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.