Macros & active content
High: primary malware vector in Office docs
Strip from all inbound files

Sanitized
Embedded objects / OLE
High: can contain hidden executable payloads
Remove embedded objects
Sanitized
External URL references
Medium: used for beaconing, credential harvesting
Remove hyperlinks; preserve display text
Sanitized
JavaScript in PDFs
High: executes on open in vulnerable readers
Strip all PDF JavaScript
Sanitized
Document metadata
Low to Medium: data leakage; some exploits via metadata
Strip metadata; preserve document content
Sanitized
Embedded images
Low: potential steganographic payload carrier
Regenerate via CDR; remove hidden content
Sanitized
Malformed file structure
High: malformation itself is an exploit technique
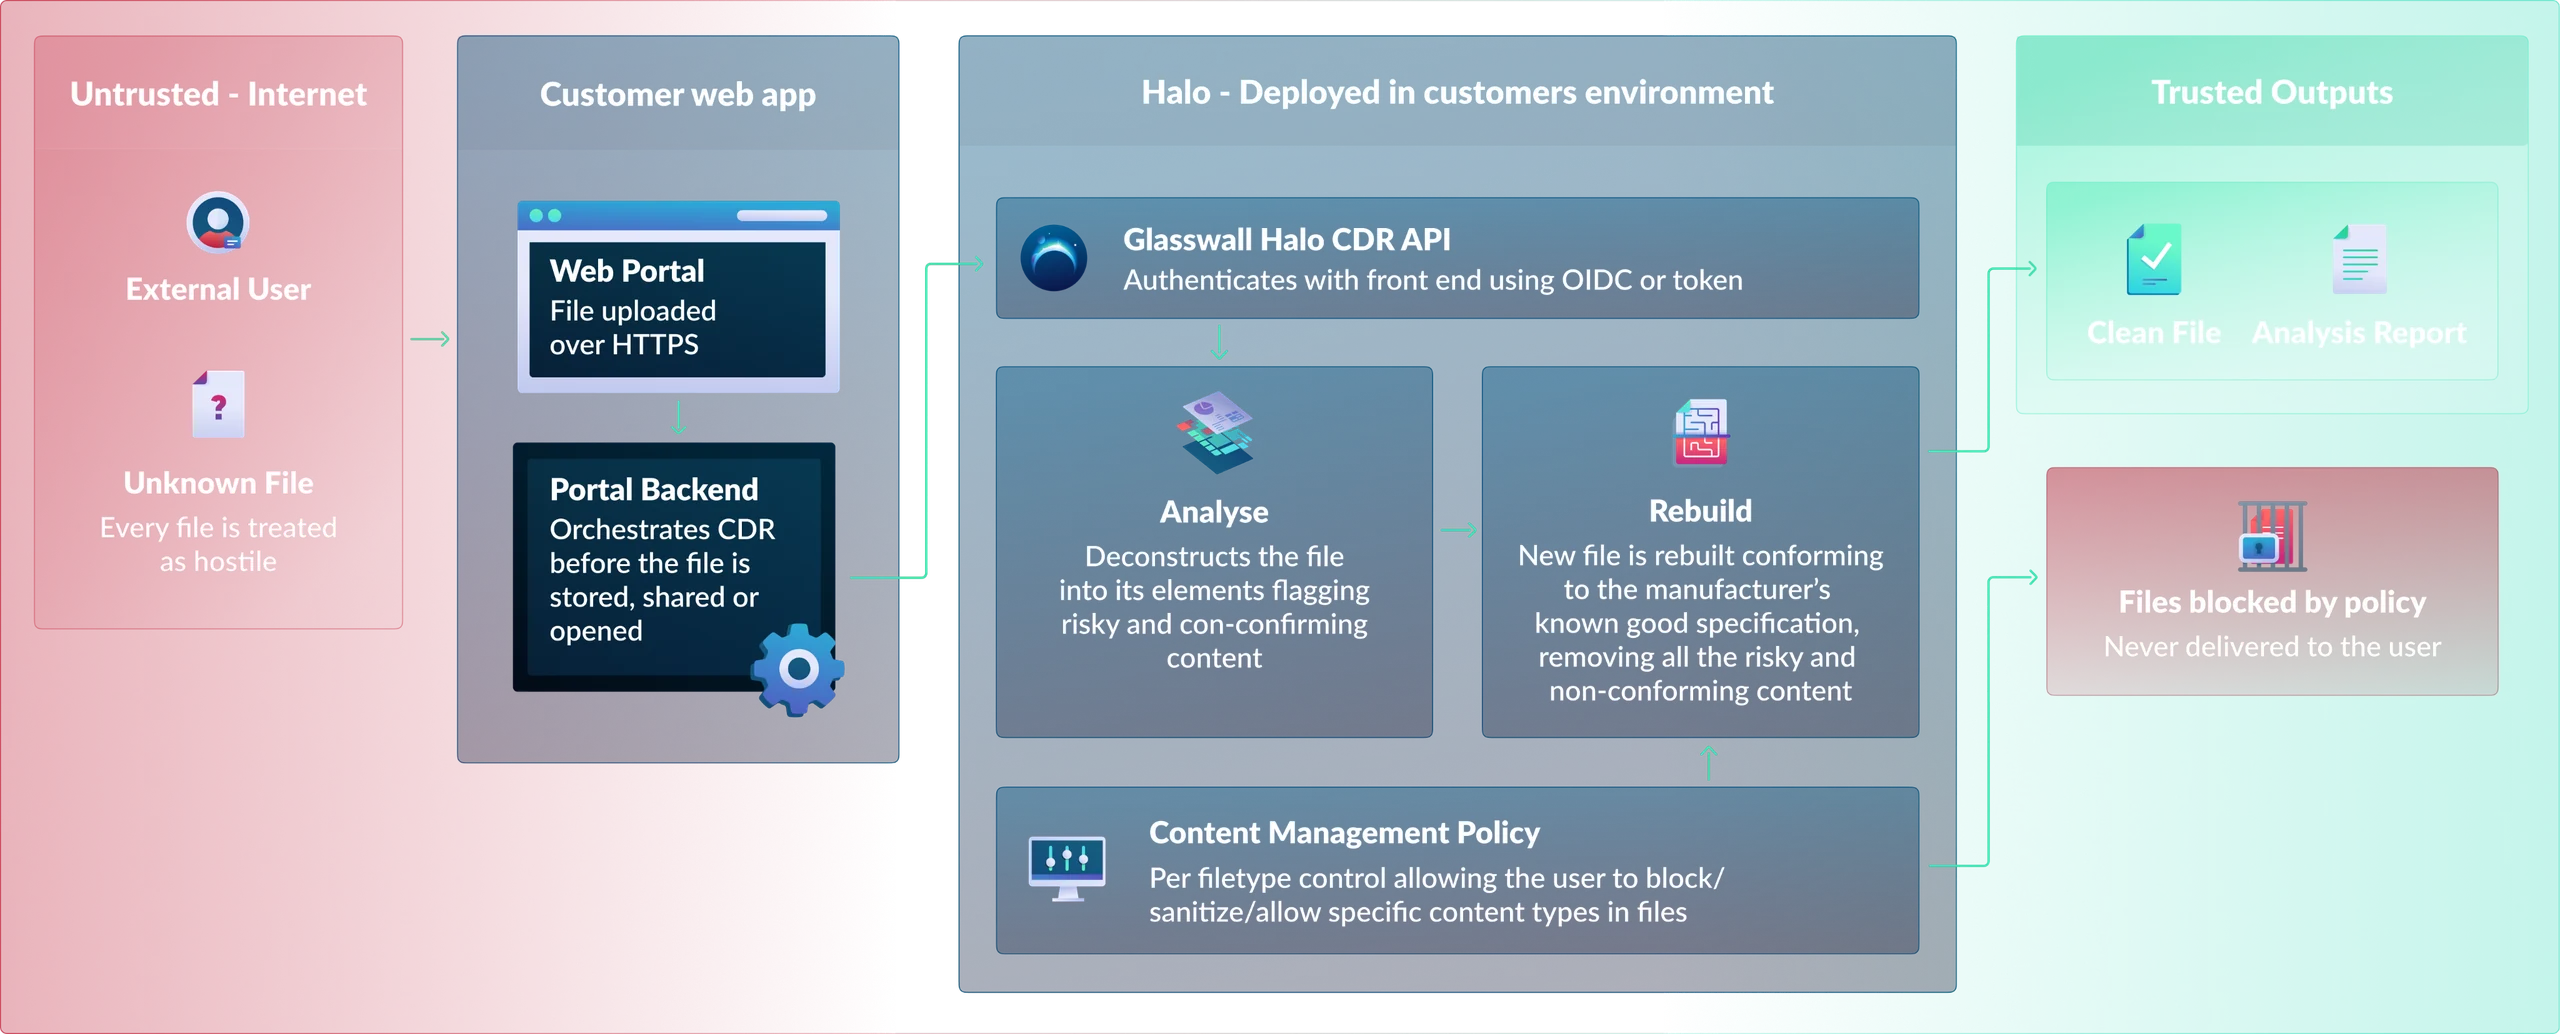
Quarantine; flag for manual review

Quarantined
Executables (.exe, .dll)
Critical: never acceptable in a document portal
Block at policy level; reject upload

Blocked