What is DORA? The Digital Operational Resilience Act
There is a line in DORA's technical standards that most financial institutions have never mapped to a named control. It is eight words long, it applies to every entity in scope, and it is the reason file security has moved from a hygiene topic to a board-level evidence problem.
“the identification of security measures against malicious codes”
That is Article 11(2)(d) of Commission Delegated Regulation (EU) 2024/1774, the regulatory technical standard that expands DORA's ICT risk management requirements. It does not name a technology. It does not name a vendor. What it does is place a documented obligation on the firm to identify what its measures against malicious code actually are, and to defend that identification when a supervisor asks.
For most banks, insurers and investment firms, the honest answer today is a detection stack: antivirus, sandboxing, an email gateway. Those are real controls. But they produce one kind of evidence, which is what they caught, and DORA's question is closer to the opposite. It asks what measure you have identified, whether it operates, and what residual risk remains on the file paths into your critical services.
This resource walks through what DORA requires, maps the regulation's actual wording to what Content Disarm and Reconstruction can demonstrate, and sets out the BFSI workflows where that mapping matters most.
About DORA
DORA is Regulation (EU) 2022/2554. It has applied since 17 January 2025. Because it is a regulation rather than a directive, it took effect directly in every Member State on the same day, without national transposition.
Roughly 22,000 financial entities are in scope across some 20 categories: credit, payment and electronic money institutions; investment firms, trading venues, central counterparties and securities depositories; insurers, reinsurers and intermediaries; crypto-asset service providers; fund managers and occupational pension institutions; credit rating agencies and crowdfunding platforms. It also reaches the ICT providers serving them, and a non-EU group with an authorized EU subsidiary is in scope through that subsidiary.
The regulation rests on five pillars: ICT risk management, incident management and reporting, digital operational resilience testing, ICT third-party risk, and information sharing. For a CISO, three consequences matter more than the pillar structure:
The management body is accountable. ICT risk sits with the board under Article 5, not with the security function alone. Control choices need to be explicable upward.
The clock on incidents is four hours. Initial notification of a major incident is due within four hours of classification and no later than 24 hours after detection, followed by an intermediate report at 72 hours and a final report within a month. Classification has to be fast and evidenced.
The detail lives in the technical standards. The regulation states general duties. Delegated Regulation 2024/1774 turns them into specific, testable requirements. That is where supervisory questions originate, and it is where the file layer appears.
Proportionality applies throughout, with a simplified framework for smaller entities. Proportionate does not mean optional. It means the depth of your controls has to be defensible against your own risk profile.
Why the file layer is where BFSI struggles
Consider what a financial institution ingests on an ordinary Tuesday. Mortgage applications with scanned identity documents. Claims evidence photographed by policyholders. KYC packs from correspondent banks. Invoices and payment instructions from suppliers. Board packs, term sheets and spreadsheets from external counsel. Every one is a file from an untrusted source, arriving at a process with a defined tolerance for disruption.
Detection-based controls answer a single question about each of those files, and they answer it probabilistically: "Have I seen something like this before?"
That is a reasonable question for known threats. It is a weaker one for a novel file, a deliberately malformed structure, a polyglot, an evasive payload that waits out a sandbox, or active content that is technically legitimate but unnecessary. When the answer is uncertain, the firm chooses between letting the file through and blocking it. Blocking a customer's mortgage document is not a neutral act. It is operational friction inside an important business service, which is precisely what DORA asks firms to measure and control.
So the CISO ends up holding two uncomfortable positions at once. Residual risk they cannot quantify, and false positives that damage the customer experience in the services the regulator cares most about.
How CDR helps BFSI CISOs address it
Content Disarm and Reconstruction takes a Zero Trust position on files. It does not try to decide whether a file is malicious. It treats every file as untrusted and rebuilds it to a known-good state, which means the outcome does not depend on having seen the threat before.
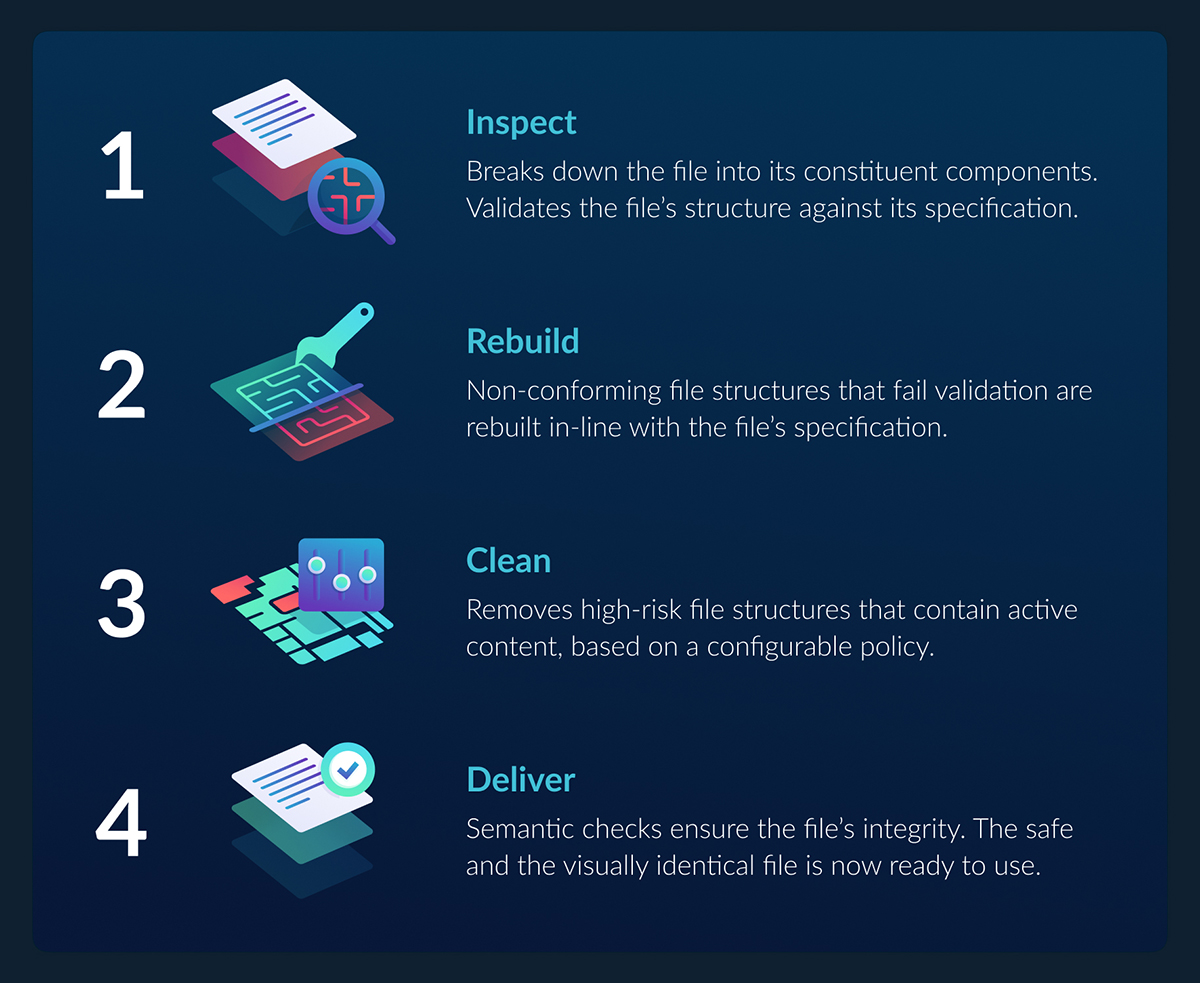
Glasswall CDR runs a four-stage process on every file:
Inspect. The file format is deconstructed into its document object model and validated against the manufacturer's specification.
Rebuild. Unknown, invalid or non-conforming structures are repaired to specification.
Clean. High-risk active content such as macros, embedded objects and scripts is removed according to policy.
Deliver. The rebuilt file passes semantic verification and is returned to the user in a safe, fully usable form, together with a processing report.
For a DORA program, the significant output is not only the clean file. It is the processing report. Every file produces a record of what was inspected, what was non-conforming, what was removed and under which policy. That converts a security control into an auditable one, and it is the difference between telling a supervisor that you have a measure against malicious code and showing them that it ran, on this file, at this time, under this configuration.
Three properties matter to a CISO building a DORA case:
It is deterministic. The same file under the same policy produces the same outcome. That is a control you can describe in a framework document, test on a schedule and evidence consistently.
It produces per-file evidence. Not aggregate detection statistics, but a record attached to each transaction flowing through an important business service.
It preserves the business process. Users receive a working document rather than a quarantine notice, so the control does not create the operational disruption DORA exists to prevent.
Mapping CDR to the actual wording of DORA
This is the table to bring to a control mapping workshop. The middle column quotes the regulation and its technical standards directly. The right column is what Glasswall CDR puts on the table as evidence.
Provision
What the regulation actually say
What Glasswall CDR lets you evidence
RTS 2024/1774 Art. 11(2)(d)
“the identification of security measures against malicious codes”
A named, documented control applied to every supported inbound file, with policy configuration and per-file processing reports as proof it operated
RTS 2024/1774 Art. 11(2)(c)
“the identification of security measures to ensure that only authorised software is installed in ICT systems and endpoint devices”
Macros, embedded objects, scripts and other executable content removed from documents by policy, so unauthorized code cannot reach an endpoint inside a file
RTS 2024/1774 Art. 11(2)(i)
“the identification and implementation of security measures to prevent data loss and leakage for systems and endpoint devices”
Embedded objects, tracked changes and hidden metadata stripped on egress as well as ingress, with a record of what was removed
RTS 2024/1774 Art. 11(2)(k)
“for ICT assets or services operated by an ICT third-party service provider, the identification and implementation of requirements to maintain digital operational resilience”
A consistent file-layer control applied to third-party file exchange, independent of the supplier's own security posture
DORA Art. 9(2)
“design, procure and implement ICT security policies, procedures, protocols and tools that aim to ensure the resilience, continuity and availability of ICT systems, in particular for those supporting critical or important functions”
A procured, deployed and configurable tool sitting on the file paths into critical or important functions, with documented architecture
DORA Art. 9(3)(a)
“ensure the security of the means of transfer of data”
Files validated and rebuilt to specification at the point of transfer, across email, web, API and managed file transfer
DORA Art. 9(3)(b)
“minimise the risk of corruption or loss of data, unauthorised access and technical flaws”
Malformed and non-conforming file structures repaired to the manufacturer's specification rather than passed downstream
DORA Art. 8(1)
“identify, classify and adequately document all ICT supported business functions … the information assets and ICT assets supporting those functions”
File ingress points enumerated as part of the control, giving a documented map of which business functions ingest external content
DORA Art. 10(1)
“mechanisms to promptly detect anomalous activities … including ICT network performance issues and ICT-related incidents”
Non-conformance telemetry on every file processed, showing which sources are sending structurally anomalous content over time
DORA Art. 12(1)(a)
“backup policies and procedures specifying the scope of the data that is subject to the backup”
Files entering archives and backups already rebuilt, so restoration does not reintroduce dormant threats
DORA Art. 30(3)(c)
contractual requirement for the provider to implement “business contingency plans and … ICT security measures, tools and policies”
Deployment on-premises, in the cloud or air-gapped, with documented availability, throughput and continuity characteristics
Two notes on using this table. Quotations are verbatim from the official English text, which uses British spellings. And DORA is risk-based, so the mapping is a demonstration of how a specific control satisfies a specific requirement in a specific workflow, not a claim that the requirement can only be met this way.
Common CDR use cases across BFSI
The deployment points follow the file, not the network. In practice, BFSI programs tend to start with one high-volume workflow, prove the control and the evidence, then extend.
BFSI workflow
The file risk
Glasswall deployment
Customer upload portals
Mortgage applications, account opening and document requests accept arbitrary files from unauthenticated or lightly authenticated users, straight into back-office systems
Halo REST API, sync or async, called by the portal before the file is stored
KYC and onboarding
Identity documents, certificates of incorporation and beneficial ownership packs arrive from correspondent banks, brokers and introducers in whatever format they use
Halo API in the onboarding pipeline, with policy tuned to preserve document fidelity for review
Claims intake (insurance)
High volume, time sensitive, emotionally charged. Photographs, invoices, medical reports and repair estimates from claimants and loss adjusters
Halo API or S3 and cloud storage connectors on the claims bucket
Email and collaboration
Attachments, and files that reach SharePoint and OneDrive without ever passing an email gateway
Halo M365 Storage Monitoring across Outlook, SharePoint and OneDrive
Web and proxy traffic
Staff downloading files from the open web, and reverse proxy paths into customer-facing applications
Halo ICAP Server with F5, FortiGate, Citrix, Cisco Secure Firewall, Squid, NGINX, VMware NSX and other ICAP-enabled devices
Third-party and supply chain file exchange
Statements of work, board packs, term sheets, payment instructions and reconciliation files from suppliers, counsel and outsourced providers
Halo API on managed file transfer, or ICAP on the gateway carrying the exchange
Payments documentation
Invoices and payment instructions, the highest value target for business email compromise and document manipulation
Halo API in the payments workflow, with strict active content policy
Applications you build
Internal tools and customer-facing apps that accept files and inherit their own file risk
Embedded Engine SDK, integrating CDR directly into the application
Third-party and supply chain risk deserves its own note
Articles 28 to 44 make ICT third-party risk the pillar with the largest ongoing administrative footprint. Article 30(2)(c) requires contractual “provisions on availability, authenticity, integrity and confidentiality in relation to the protection of data”, and for critical or important functions Article 30(3)(e) requires “the right to monitor, on an ongoing basis, the ICT third-party service provider's performance”.
Contract terms and audit rights are necessary, but they are assurances about a supplier's controls rather than controls of your own. A file arriving from a supplier is a file whose safety you have contracted for and cannot independently verify. Applying CDR at that boundary converts a contractual assurance into an enforced technical control, and RTS Article 11(2)(k) asks for precisely that: requirements to maintain digital operational resilience for assets and services operated by third parties.
The same logic applies in reverse when your own institution is the supplier, for example a custodian or an asset servicer sending files to clients. Sanitizing on egress protects the relationship and evidences integrity in both directions.
What a BFSI evidence pack looks like
When a supervisor, internal audit or a client's due diligence team asks how you address malicious code in files, a Glasswall deployment supports a documented answer built from:
A named control with a documented architecture, mapped to the file ingress points of each important business service
Policy configuration showing exactly which content types are removed, preserved or blocked, and why
Per-file processing reports evidencing that the control operated, with non-conformance detail
File risk classification and telemetry showing which sources send structurally anomalous content over time
Supported format coverage across more than 45 file formats and more than 140 extensions, with a documented policy for what falls outside it
Performance and availability data supporting the operational tolerance you set for the service, drawn from a deployment that has demonstrated throughput on the order of 186,000 files per hour and sub-second median processing
Deployment and continuity documentation for on-premises, cloud or air-gapped operation, supporting Article 30(3)(c) style questions
That pack answers the question DORA actually asks, which is not whether you bought something, but whether you identified a measure, implemented it on the paths that matter and can show it working.
Five questions worth asking internally
Which of our important business services routinely ingest files from customers, employees or third parties, and are those ingress points documented under Article 8?
What named measure addresses malicious code inside those files, and would we be comfortable writing it into our data and system security procedure under Article 11?
Can we produce per-file evidence that the measure operated, or only evidence of what it blocked?
If a file-borne incident were classified as major, could we answer the initial notification questions inside four hours?
For files arriving from third parties, are we relying on a contractual assurance where we could be enforcing a technical control?
If question three or five gives you pause, the gap is at the file layer.
See it against your own files
Book a technical briefing with our financial services team and we will work through your file ingress points, the policy configuration for each, and the evidence Glasswall CDR produces in a live workflow, including the register and Article 30 documentation your procurement team will need. Or try Glasswall CDR in the browser and watch a file get rebuilt in real time.
Riyya Ahmed
Our Senior Technical Writer and Product Marketing Manager, Riyya, is exceptional at authoring, organizing, and simplifying our product documentation. Using her keen eye for detail and wealth of experience in tech, Riyya helps our clients and partners seamlessly integrate with industry-leading Zero Trust CDR.
See what Zero Trust file protection looks like. Live, in 25 minutes.
A tailored walkthrough of how Glasswall rebuilds files to a known-good state, removes hidden threats, and provides the intelligence you need to understand file risk.
What's in the demo
See malicious files rebuilt in real time Watch Glasswall remove hidden threats and return a safe, usable files.
Integrate security without disruption See how Glasswall fits into your existing workflows and infrastructure.
Gain complete visibility into file risk Uncover threats, anomalies and hidden file intelligence.
“
Beazley's security is paramount, and this integration has significantly reinforced our cybersecurity framework.
Thank you! Your submission has been received!
Oops! Something went wrong while submitting the form.